



1. Introduction
KORG Inc. (hereinafter referred to as "the Company") accepts vulnerability reports from reporters and appropriately discloses information to our customers and users (hereinafter referred to as "Users") to maintain the security of our products and applications. This Policy applies to vulnerabilities reported to the Company by reporters who have discovered them. Please read this Policy carefully, and we ask that you agree to and comply with it prior to conducting any research.
2. Safe Harbor / Authorization
The Company welcomes investigations and reports by good-faith researchers aimed at improving cybersecurity. We consider vulnerability investigation, testing, and reporting activities conducted in compliance with the rules and scope outlined in this Policy to be authorized and legitimate conduct. The Company will not take legal action (civil lawsuits or criminal complaints) regarding unauthorized access or copyright infringement against reporters acting in good faith and within the scope of this policy. In the highly unlikely event that a third party initiates legal action regarding research or other activities conducted in compliance with this policy, the Company will confirm and state that the reporter's actions were conducted in cooperation with our official program.
3. Scope / Out of Scope
The scope of this Vulnerability Disclosure Policy includes products and applications under the following brands:
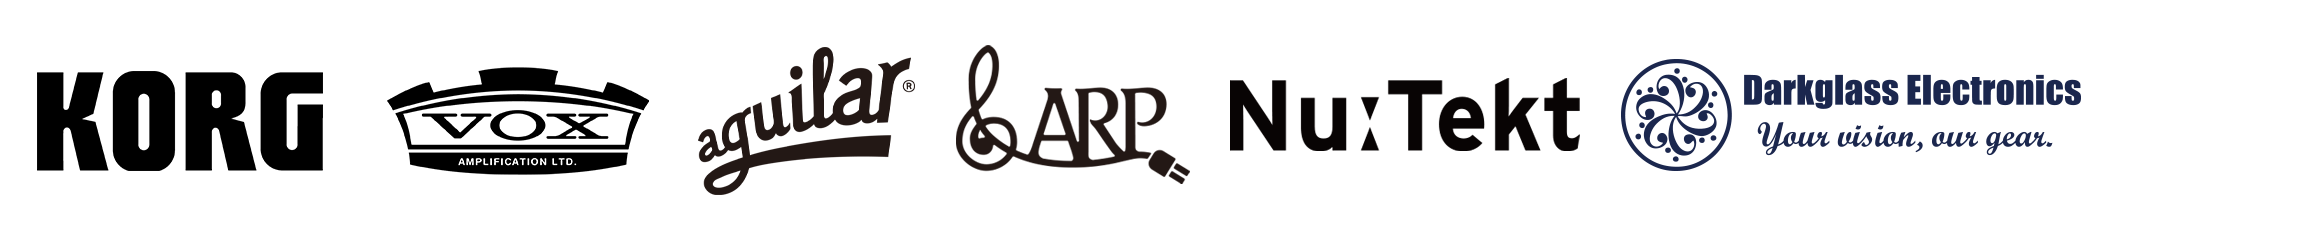
We also accept vulnerability reports for discontinued products and End-of-Life (EOL) products. However, please note that we may be unable to investigate or provide a resolution for them.
Note that vulnerability information that the Company has already publicly disclosed and for which a remediation patch has been provided is out of scope. Third-party systems and hosting environments not managed by the Company are also out of scope.
4. Rules of Engagement
To protect the Company and our Users, please adhere to the following rules when investigating and reporting vulnerabilities.
(1) Confidentiality and Coordinated Disclosure
Please comply with the following confidentiality requirements:
- Vulnerability Confidentiality (Embargo): Until the Company provides a resolution (e.g., a patch) and officially publishes the information, please do not disclose or leak any information regarding the discovered vulnerability (including its existence, status, and proof-of-concept code) to any third party without our permission. We will coordinate with the reporter regarding the timing and content of the public disclosure. - Communication Confidentiality: Disclosing, reproducing, or secondarily utilizing the contents of communications (such as emails, in whole or in part) exchanged between the Company and the reporter to any third party without our prior permission is strictly prohibited.
(2) Testing Restrictions
When investigating and testing for vulnerabilities, the following activities are strictly prohibited:
- Prohibition of Destructive or Malicious Testing: Testing methods that impair system availability (such as DoS/DDoS attacks), or those that involve accessing, viewing, modifying, or deleting data belonging to others (including personal data). - Prohibition of Out-of-Scope Attack Methods: Physical security attacks against the Company's facilities or related infrastructure, social engineering (e.g., phishing) against Company employees or customers, any actions that disrupt the operation of our services or degrade service quality, and any other actions that place an excessive load on our systems. - Compliance with Laws and Prevention of Harm: Do not cause damage, harm, or loss to any individual or organization at any stage of the investigation, report creation, or discussions with the Company. Always comply with applicable national and local laws and regulations.
5. How to Submit a Report
If you discover a vulnerability in an eligible product or application, please report it to our contact window using the reporting form below.
By submitting vulnerability information through this reporting form, you consent to the Company contacting you when necessary.
When reporting, please provide the following information:
- Reporter's Information:
(Name or handle, organization name, country/region, email address, etc.)
- Name and version of the Company's product and application containing the vulnerability:
- Environment, version, and conditions under which the vulnerability is reproducible:
(OS name and version of the PC or mobile device, digital connection type, names of connected devices, etc.)
- Type of vulnerability (if known):
(e.g., Buffer Overflow, Remote Code Execution)
- Potential impact of the vulnerability (if known):
(e.g., Personal data leakage)
- Detailed steps to reproduce the vulnerability:
- Proof of Concept (PoC) or exploit code (if known):
The personal information you provide will be used solely for the purposes of receiving vulnerability reports, investigating and evaluating them, implementing countermeasures, and communicating with you. It will not be used beyond the scope necessary to achieve these purposes.
Reporting Form
This reporting form is encrypted and protected via HTTPS.
This reporting form also accepts anonymous reports.
Information exchange with the reporter after reporting to our contact window will be conducted via email.
[Notice: Encryption of Confidential Information]
When your report includes sensitive information such as detailed vulnerability descriptions or Proof of Concept (PoC) code, please encrypt it using our PGP public key and paste the generated encrypted text (ASCII Armor format) into the input field of the reporting form.
PGP Key ID: B5AF876429CB0355
PGP Key Type: rsa4096
Creation Date: 2026-08-07
Expiration Date: 2027-08-07
PGP Fingerprint: FF63 A37E D613 1473 F741 BE11 B5AF 8764 29CB 0355
PGP Public Key
6. Our Response Process
The Company will respond to reported vulnerabilities according to the following steps.
(1) Receipt and Triage
- Acknowledgment of Receipt: As a general rule, we will notify you by email within 5 business days that we have received your report (this may be delayed due to extended holidays at our global locations, a high volume of reports, or other unavoidable circumstances).
- Initial Evaluation (Triage): We will review the reported content and make our best effort to complete the initial evaluation of the vulnerability within a target of 14 business days.
(2) Investigation and Mitigation
- Investigation and Patch Development: The development department of the relevant product will promptly conduct an investigation, and we will develop and provide a security patch (fix program) as swiftly as possible, depending on the severity and complexity of the vulnerability. - Collaboration with Third-Party Organizations: To verify the vulnerability and identify the scope of its impact, the Company may, if deemed necessary, provide information to and entrust analysis to a specialized third-party organization bound by appropriate confidentiality obligations. - Status Reporting: While working toward a resolution, we will report the current progress to you if there are changes in the situation, or at a maximum of every 30 days since the last contact, and will provide a final report once the issue is completely resolved.
(3) Information Sharing and Public Disclosure
- Information Sharing with Public Authorities: If it is confirmed that the reported vulnerability information is actively being exploited, or if it constitutes a severe incident, the Company may be obligated to share such information with the European Union Agency for Cybersecurity (ENISA), national CSIRTs, coordinating bodies, etc., based on legal requirements of respective countries (such as the European Cyber Resilience Act). - Public Disclosure to Users: As soon as a security patch is ready, we will publicly disclose the vulnerability description, affected products, severity, and remediation steps on our website's News page (and various SNS, etc.) (Note: to be adjusted to match Web operational policies) to notify our Users. - Information Sharing with Upstream Developers: If the reported vulnerability originates from a third-party component or open-source software integrated into our products, the Company may provide the vulnerability information or remediation measures to the maintainer (developer) of the relevant component to enhance the security of the entire ecosystem. - Disclosure Delays and Restrictions: Given the nature of a vulnerability, if there are legitimate reasons where the risks of disclosure outweigh the benefits—such as the need to secure a patch application period—we may exceptionally delay the disclosure of information or keep it undisclosed.
7. Reward / Bounty
The Company does not provide rewards (monetary, physical goods, etc.) to reporters, nor do we operate a bug bounty program, regardless of the nature of the vulnerability.
8. Privacy / Changes
Regarding our policy on the handling of reporters' personal data, please refer to the "Privacy Policy" on our website.
Privacy Policy
https://www.korg.com/corporate/privacy/
This Vulnerability Disclosure Policy is subject to change without prior notice. The revised policy shall become effective from the time it is displayed on this page.
Enactment Date: September 1, 2026
Copyright © 2026 KORG Inc. All Rights Reserved.
Choose Your Location 